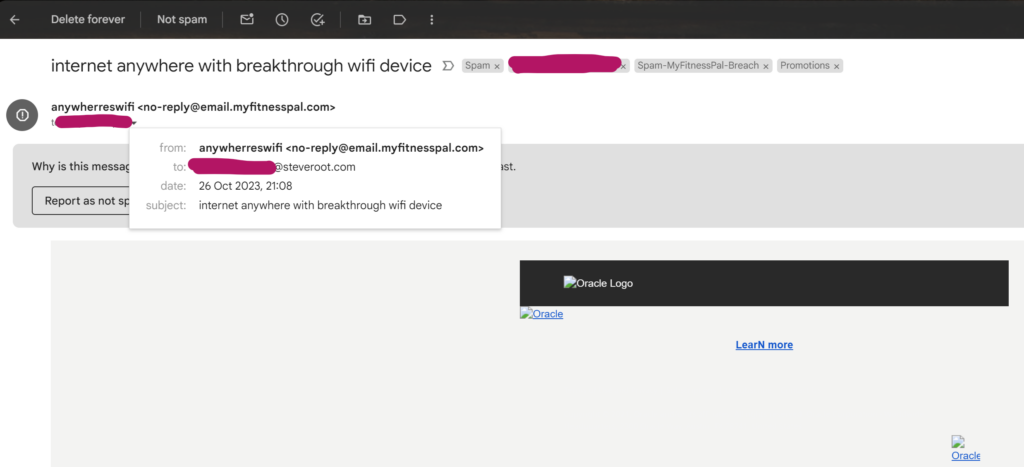
I use different email addresses for different services, which is how I know this spam email obtained the address from the myfitnesspal.com breach. The address is still being bought and sold. The spam filters pick up most of these but it’s still annoying.
I just noticed some interesting features about this spam email though;
first: They are using the send address as email.myfitnesspal.com. I know that sender email address displayed by an email client is not proof of the sender, it’s simply what the sender says it is. I could send an email pretending to be from you.
Interesting to me is that they not only bought my email address to send spam to, they know exactly where the address came from and are trying to improve clicks by pretending to be something the receiver would recognise.
second: they seem to be faking DKIM validation. DKIM is a system for proving the sender domain is who they claim to be. Every email is ‘signed’ by the sending server and the receiving server can check the signature is valid. Emails have ‘headers’ that record the path the email has taken across the internet and this email seems to fake DKIM validation earlier in it’s history
Authentication-Results: mail.iss.as9143.net; spf=pass (142.0.83.125;bounce.email.myfitnesspal.com); dkim=pass header.d=email.myfitnesspal.com; dkim=pass header.d=esp1.co; dmarc=none header.from=email.myfitnesspal.com (dis=no_record)the last hops, probably the real origin, fails the DKIM check though
Authentication-Results: mx.zohomail.eu; dkim=fail header.i=no-reply@email.myfitnesspal.com; spf=none (zohomail.eu: 43.135.178.51 is neither permitted nor denied by domain of r190.contact.loccitane.com)

smtp.mailfrom=Rp1G1Iu3hm3ZcANe07Tt9M3jq@r190.contact.loccitane.com; dmarc=fail(p=quarantine dis=quarantine) header.from=email.myfitnesspal.com

Return-Path: <Rp1G1Iu3hm3ZcANe07Tt9M3jq@r190.contact.loccitane.com>

Received: from envelope.catholicvote.org (43.135.178.51 [43.135.178.51]) by mx.zoho.eu with SMTP id 1698370431825475.96595520210894; Fri, 27 Oct 2023 03:33:51 +0200 (CEST)
third: They are using assets from oracle.com. That’s common for spammers and there’s nothing the owner can do to prevent that as they’re just publicly available images.
@import url('https://www.oracle.com/oce/dc/assets/CONT90096A93EBA646988FCB11EBA125B022/native/tb-oracle-sans-font.css?family=Oracle+Sans');

<img src="https://www.oracle.com/oce/dc/assets/CONT01489EC078214170985966B7D8E5C11D/native/tb-oracle-white-123x16px.png" alt="Oracle Logo" style="display:block;" width="92" border="0">
So, what is the spammer trying to get us to visit?
It seems to be a firebase url
<a href="https://firebasestorage.googleapis.com/v0/...."